
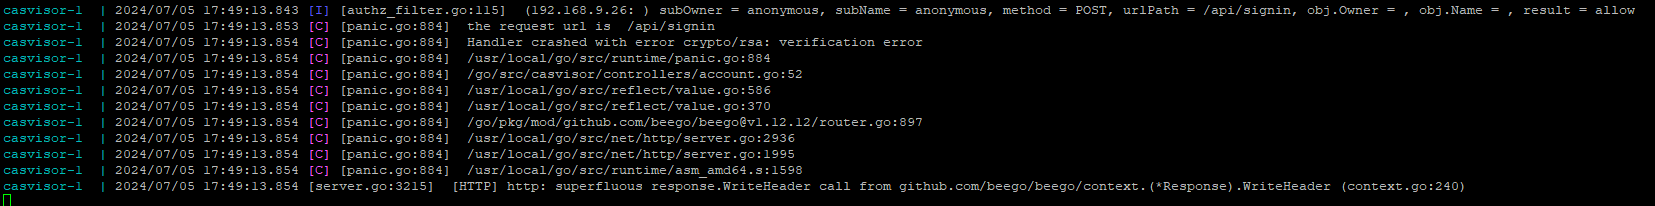

your cert-built-in should be updated to casvisor side
Would you have any example of Docker Compose to help me in this case? Would I have to use nginx to use the certificate?
use all-in-one image, it's much easier
I managed to get past this part, now I'm trying to run casvisor and see how it works, but after I enter my login, there's a white screen, I don't know if I should install something else or the problem is in my callback url
Now even with the certificate and the correct settings, it gives the same rsa problem again
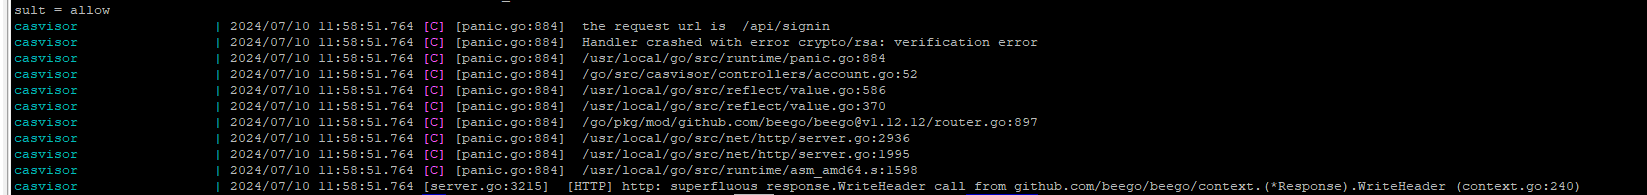
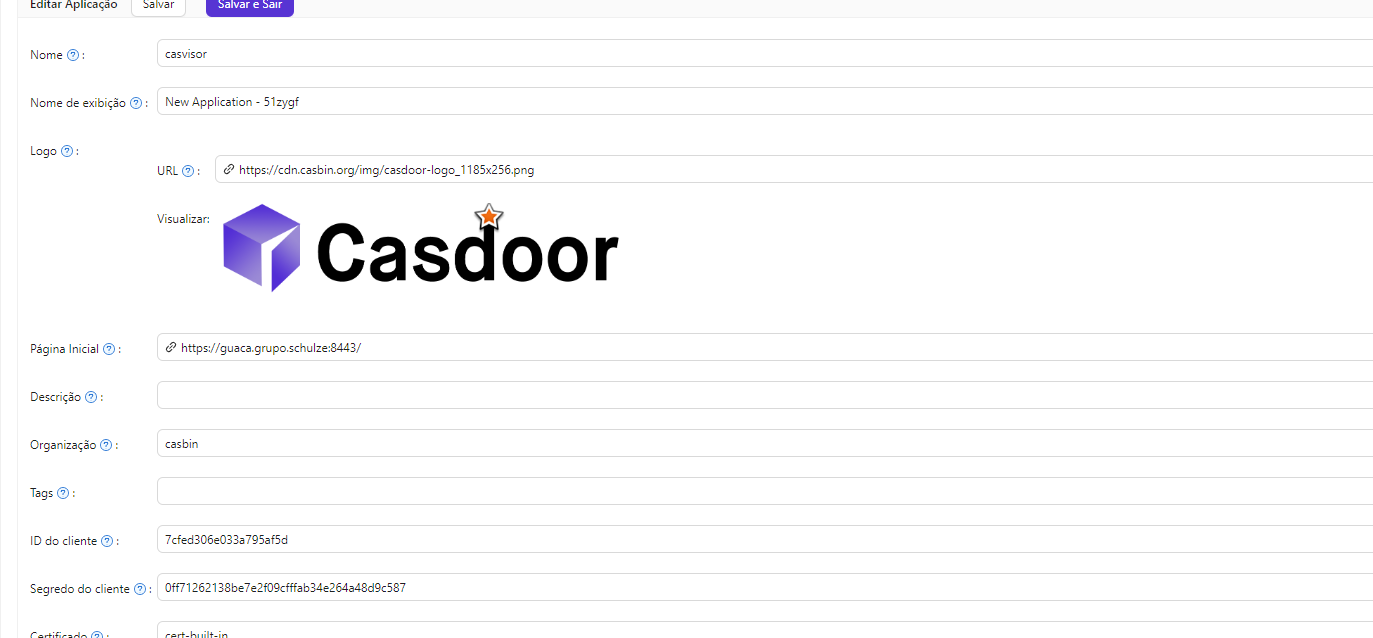
I made some progress (I managed to change the error)
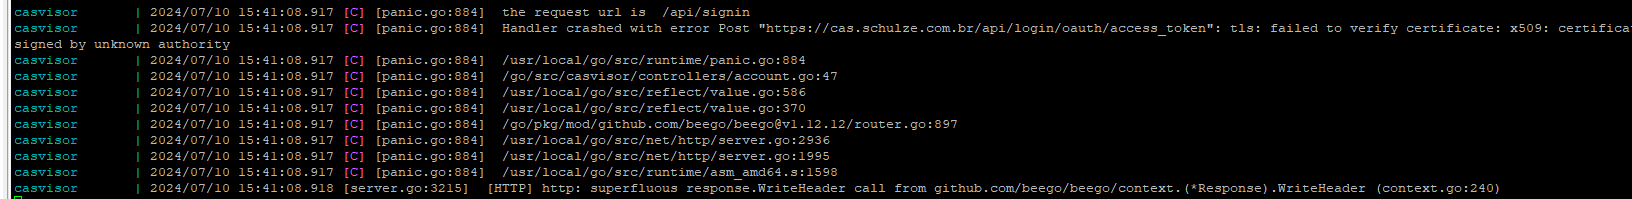
I discovered that casvisor does not accept a self-signed certificate, only CA, I used CA and managed to open the application, now I have this problem when testing a connection but I think it has to do with the guacamole
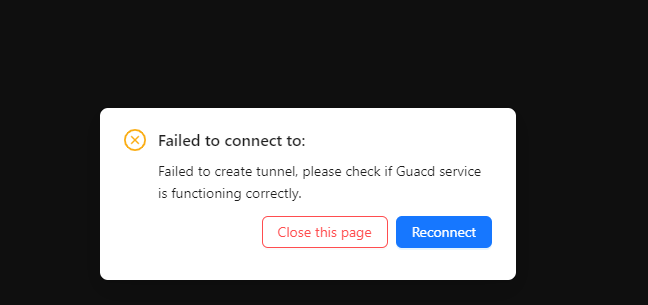
use http then
How do I enable LDAP users to connect/create RDP access on the casvisor? I already have ldap synchronized but I don't know where to enable these permissions
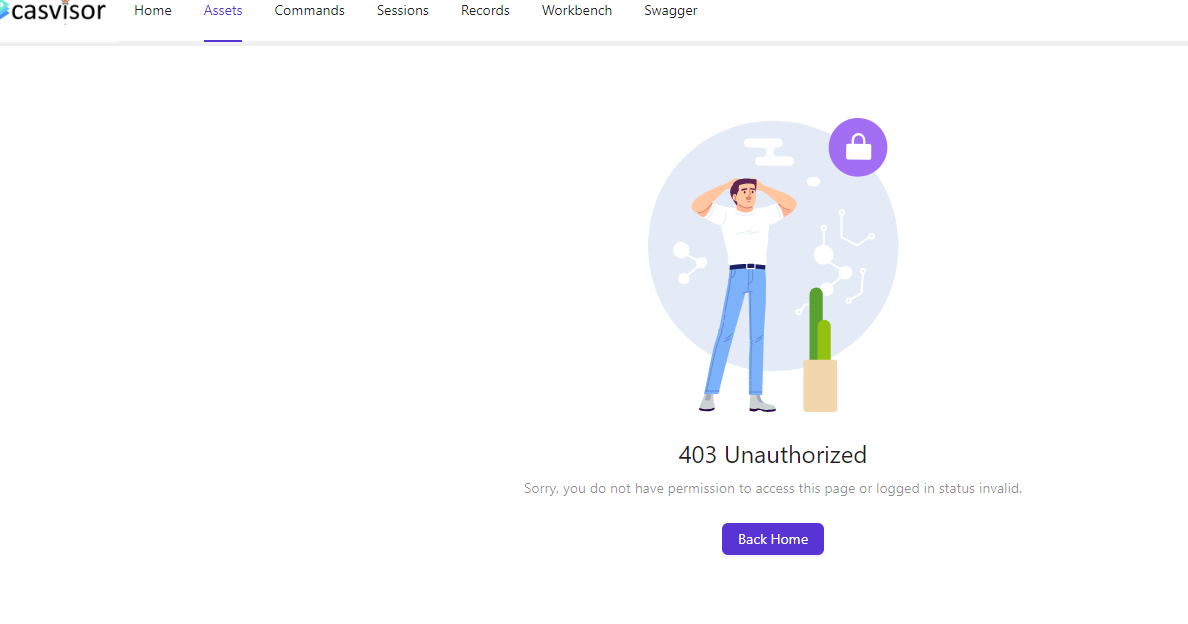
@hsluoyz can you help me?
Ah, I ended up sending it to the casdoor bug reports channel, I'll test it and get back to you soon, thank you
don't work, now it triggers a lot of logs, I think it's bringing the subowner and the wrong subname too, before it brought the subOwner as the organization name and subName as the username

I could be wrong in my comment above but anyway, it is triggering a lot of logs that come with the test user and still the error persists, I don't know if I should do anything else on my part
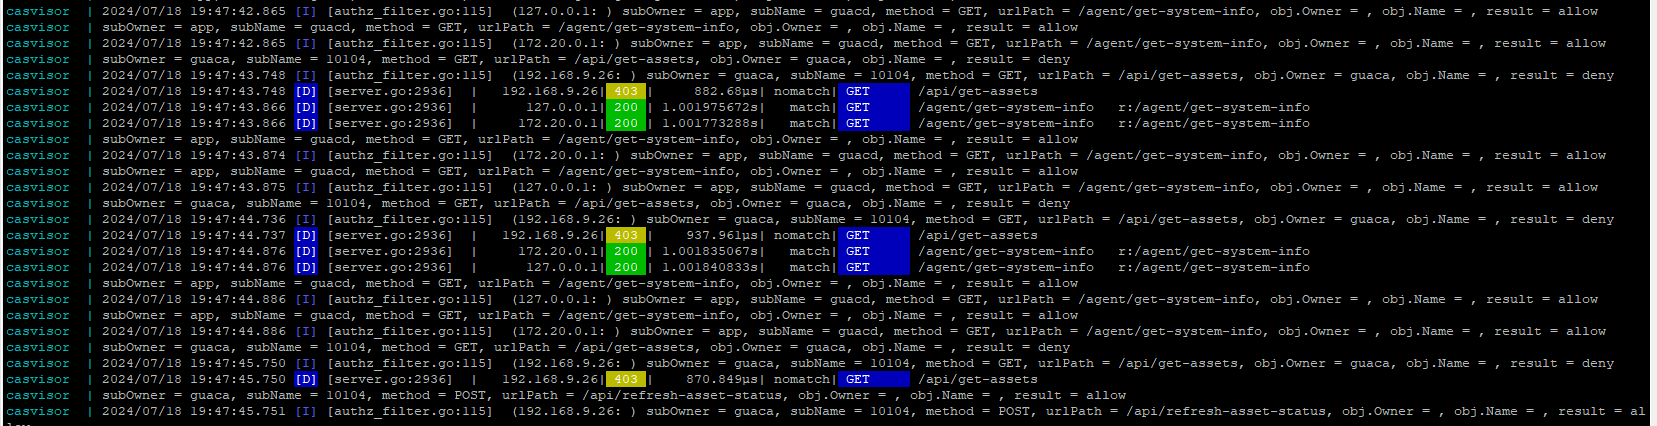
It worked, I'll let you know anything
tks
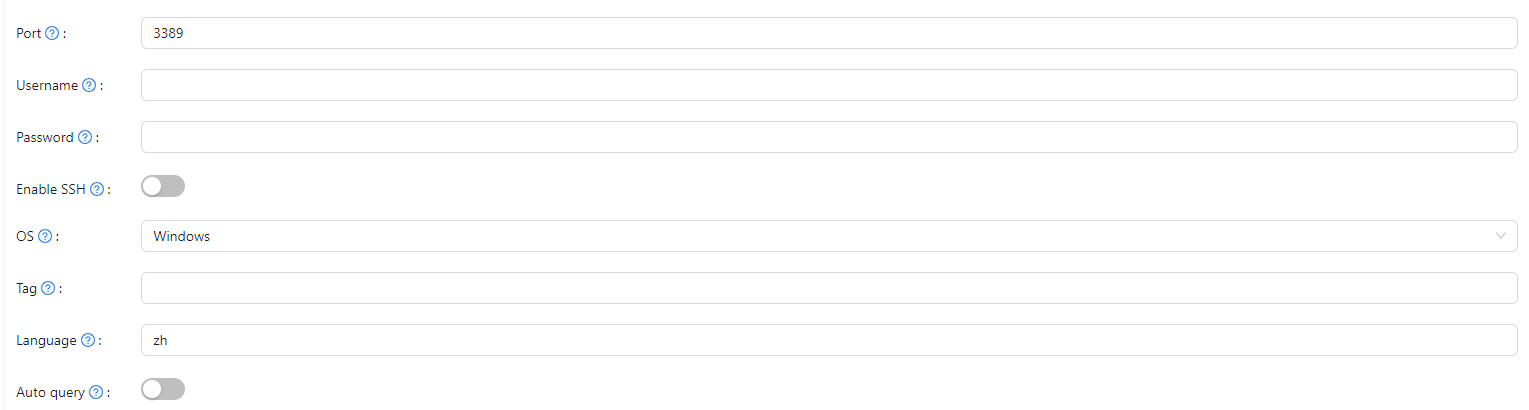
Well, the connection via ssh works normally, the problem now is the RDP connection, in addition to the security flaw going through the username and password in the application's url, it gives an authentication error when trying to log in, leaving the fields empty. Even if the password is correct, it gives the same error. To reproduce, simply create an RDP connection and leave the "username and password" fields empty
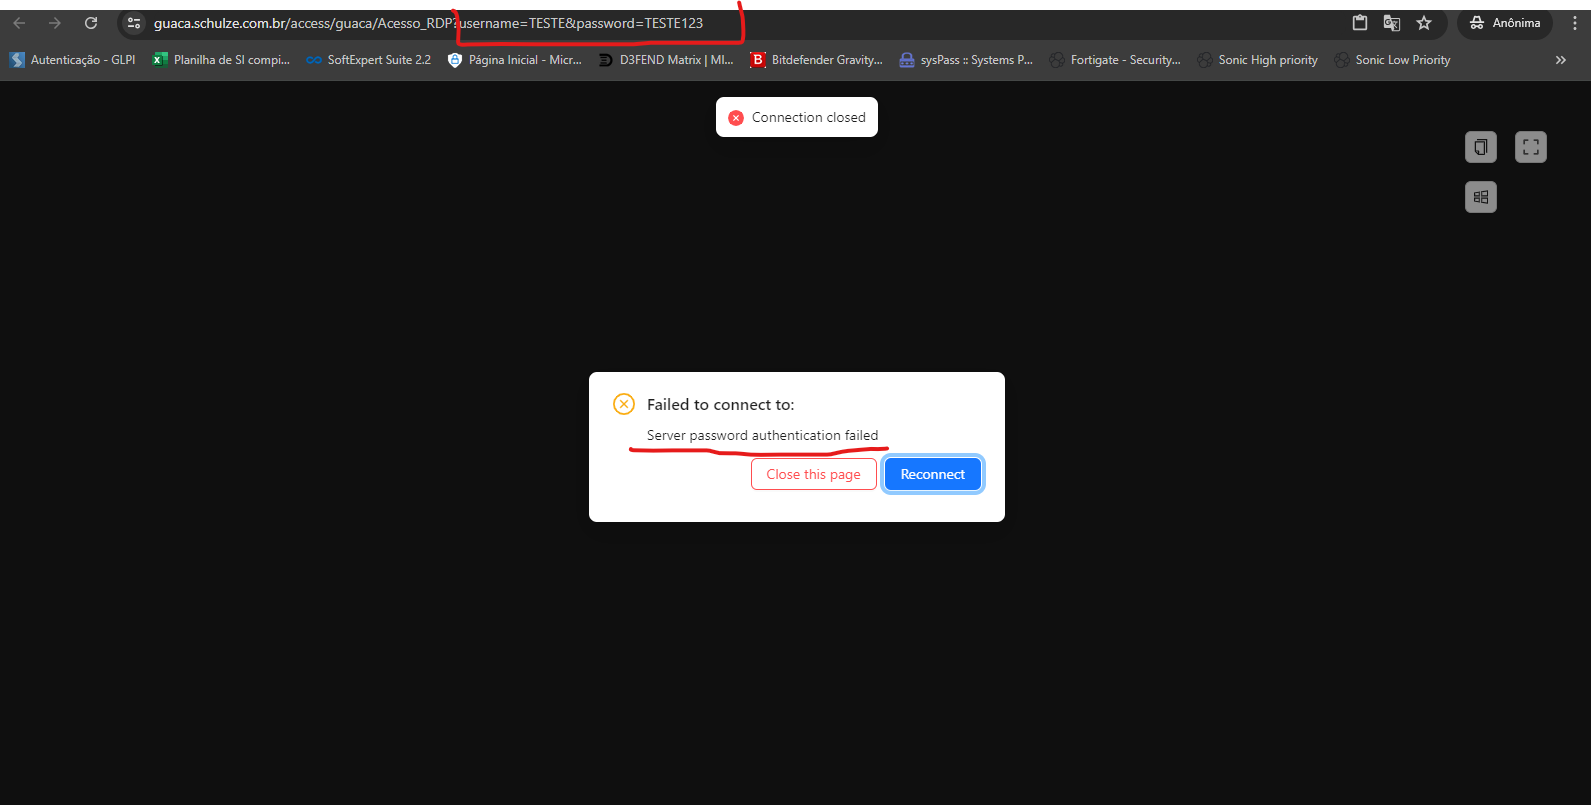
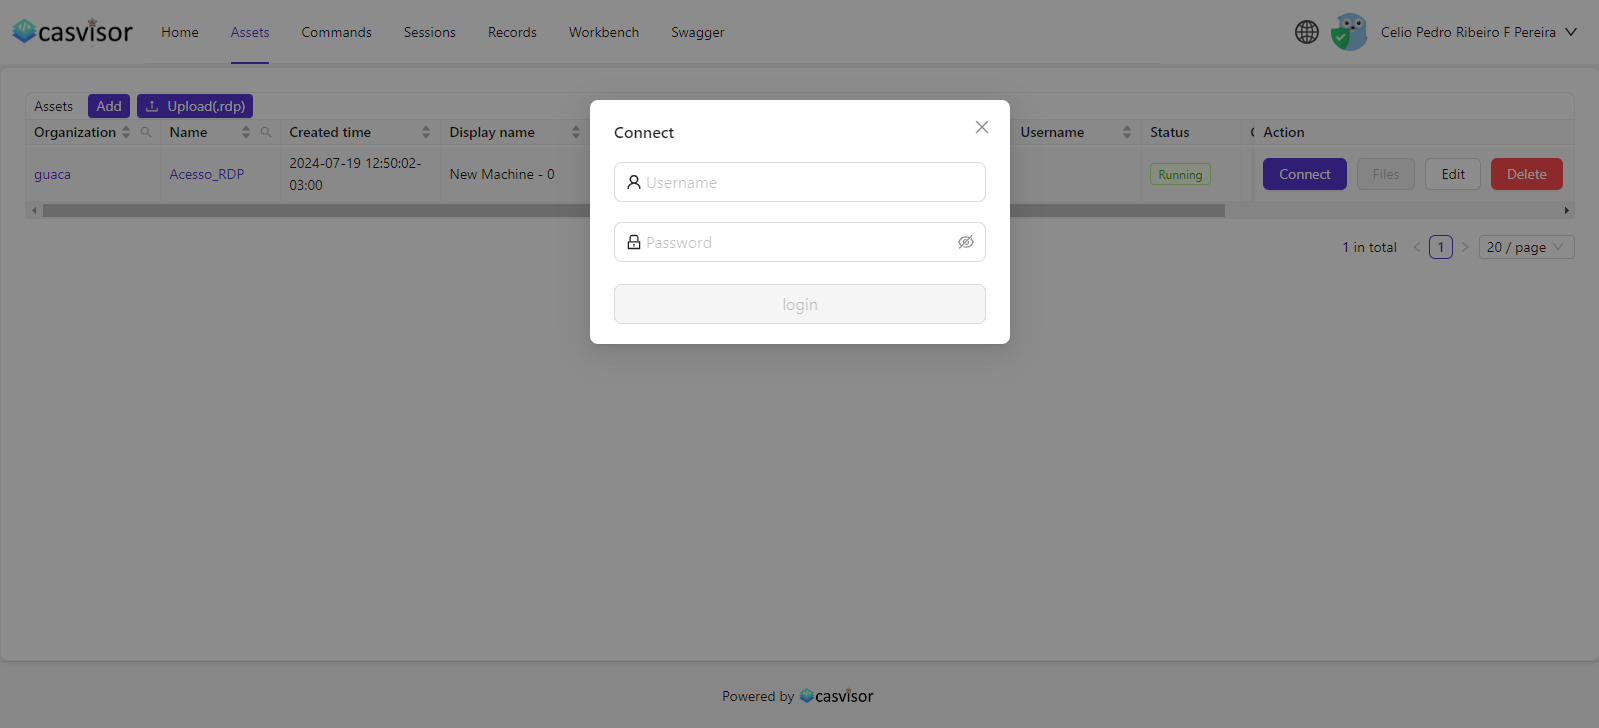
I believe it is this login and password pop up that is not passing correctly to the back end
