rainydev
RainyDev
Thanks! I managed to get my users migrated and in the correct org now. Is there somewhere a guide on how to restrict an OIDC App on certain roles/groups?
I want to have a lets say cloud_users group which shall have access on the Cloud Application
So if a user doesnt have the group he cant sign in/the application doesnt show up on the user dashboard
Design Question:
Is it recommended to always create a new org or should I use the built-in org for the primary/"first" organization?
I suppose keep the built-in only for system dependencies/applications and have the users sit in a different org, right?
Alright, thanks! 🙂
Do you happen to know by any chance if there's some way to get rid of the inbuilt database/organization and set a new default Org?
Switzerland 🙂
Im completely new to Casbin and elaborating it 🙂
Thanks mate and you are aswell 🙂
It does indeed work, I get redirected to http://localhost:9000/callback?code=XXXXXXX&state=casdoor so that seems to work 🙂
And entering a wrong password on purpose gets denied so that seems to work perfectly fine. Tysm!
Hold up, when I switched to "pbkdf2-django" instead of "pbkdf2-salt" it did work indeed. Let me try deleting all users, syncing again and then see if I can still login to an example application
I dont know if this uses sha256 it only has those options
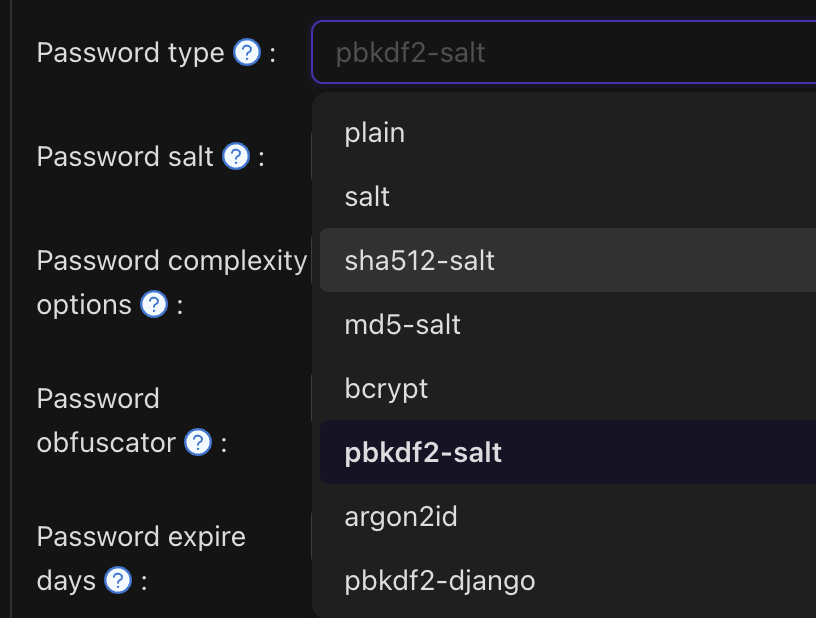
"pbkdf2_sha256$720000$Rh" this is the beginning of a password entry in the database
so its indeed pbkdf2_sha256
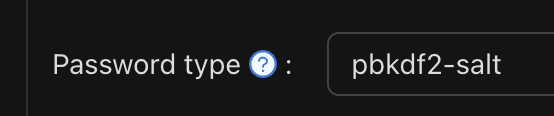
Okay unfortunately password sync doesnt seem to work.
I configured following:
In Org Setting:
Password type: pbkdf2-salt (should be the one authentik is using)
Password salt Set to the AUTHENTIK_SECRET_KEY
Syncer:
password (origin field name) -> Password (casbin)
Shouldnt that work? Any Ideas?
I might have an idea
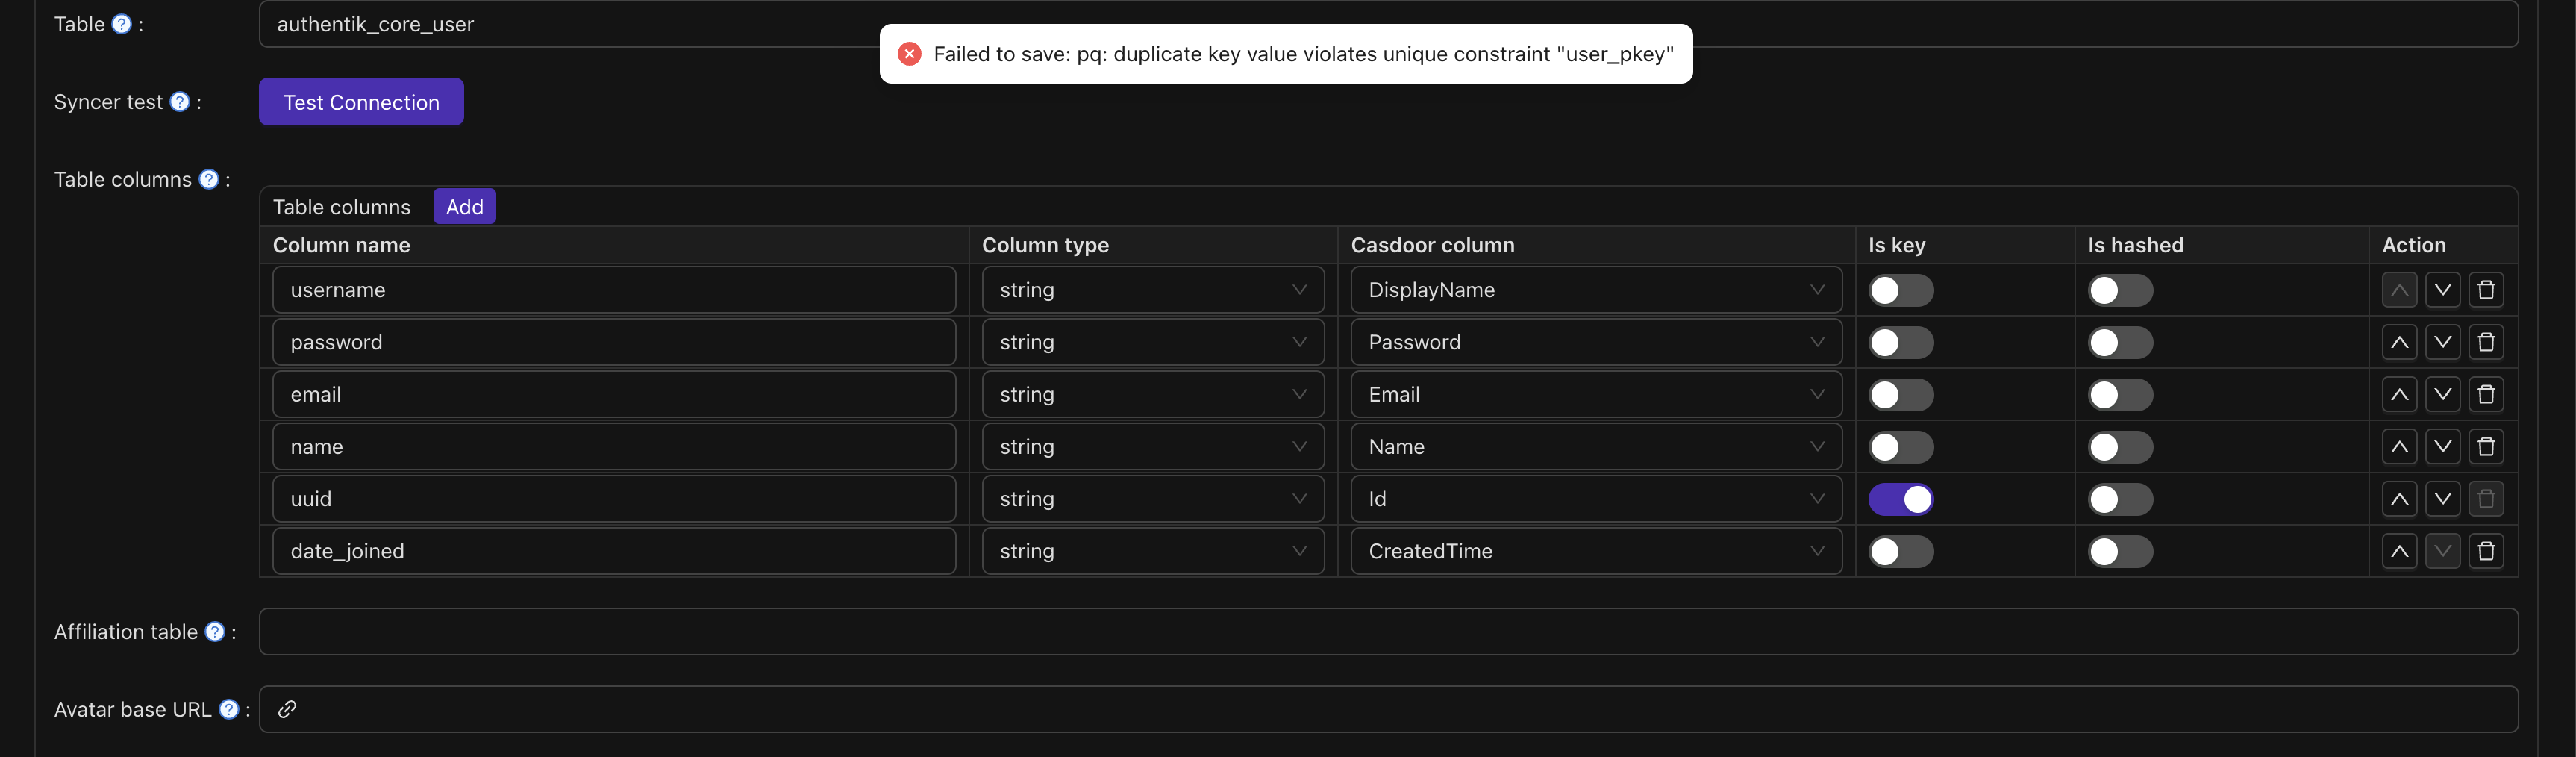
haha thats funny, it failed because I had multiple users with the same "name" Field (for testing purposes). That failed the query and when i just attached 1, 2, 3 suffix to different accounts it did import correctly. now I just have to see if password sync works correctly, thank you 🙂
I just checked, there are no duplicate UUID's in the existing authentik users table and also no existing user in casdoor with a same UUID
No duplicates UUIDs in the source and also no overlap in the existing users in casdoor (only initial admin anyways)
Hi there, I'm trying to migrate from authentik and trying to sync my existing users (they need to have the same id/uuid).
Im getting this error though: "Failed to save: pq: duplicate key value violates unique constraint "user_pkey""
Screenshot for table config:
Any Ideas?