hadesdevs
Angelo
@hsluoyz @dacongda thanks so much again for your reactivity, everything works as intented with my docker mail server and casdoor now, I can authenticate using OIDC without any issues. I just have to figure out how to provision accounts into docker mail server from the authenticated user, but that's another unrelated issue to casdoor
@hsluoyz I've created the following issue :
https://github.com/casdoor/casdoor/issues/3396
Exactly that
I'll do it as soon as I'm home, as it is a side project of mine and I'm currently at work. My workplace is very restrictif on what can be accessed or not.
And as I said here, I don't have enough knowledge on the casdoor codebase, I just tried to look at where the token_type_hint is used, and it came up here, and I also have never used Go before, but I think something along the lines of this should do what's written in the RFC
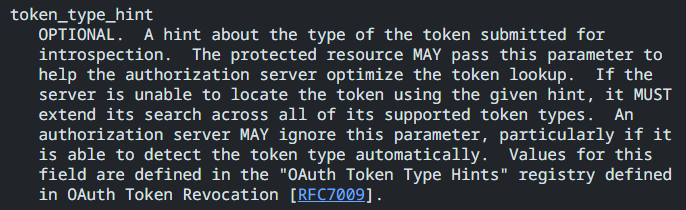
Sorry, I'll try to make it short, the token_type_hint should be optional as said in the RFC, it's not a want from my end, it's just other tools I use that expect it to be optional don't get the right response as it is a required argument right now in casdoor
@hsluoyz mainly what this section of the RFC on OIDC
I don't have any knowledge of Go or how the current code works, but from what the RFC indicated, the function named GetTokenByTokenValue in objet/token.go should be this:
func GetTokenByTokenValue(tokenValue, tokenTypeHint *string) (*Token, error) {
    switch  {
    // if no token_type_hint provided, check both access and refresh tokens
    case tokenTypeHint == nil:
    case *tokenTypeHint == "":
        token, err := GetTokenByAccessToken(tokenValue)
        if token != nil {
            return token, nil
        }
        token, err2 := GetTokenByRefreshToken(tokenValue)
        if token != nil {
            return token, nil
        }
        if err2 != nil {
            return nil, err2
        }
    // if either access_token or refresh_token is provided, only search that kind of token
    case *tokenTypeHint == "access_token":
        token, err := GetTokenByAccessToken(tokenValue)
        if err != nil {
            return nil, err
        }
        if token != nil {
            return token, nil
        }
    case *tokenTypeHint == "refresh_token":
        token, err := GetTokenByRefreshToken(tokenValue)
        if err != nil {
            return nil, err
        }
        if token != nil {
            return token, nil
        }
    }

    return nil, nil
}
I've traced it back to this commit: https://github.com/casdoor/casdoor/commit/a19060c7cb1b8761f834bdcbd6670b68f4e1139b
Why was token_type_hint even added ?
in the oauth RFC it says this attribute should be optional, whic aligns with all configs I've seen so far :