
guillaumedrevo
Hi hsluoyz, thanks for replying!
This is my example:
- p, admins, resources, read
- g, alice, admins
- g2, resource1, resources
In the Casbin Editor:
- alice, resource1, read => true
- alice, resources, read => true
If I try to enforce the same in the Casdoor integration of Casbin I have this:
- alice, resource1, read => false
- alice, resources, read => true
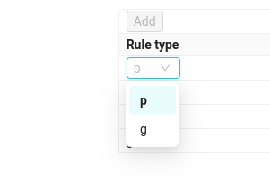
Plus, already within the webUI, I cannot set g2 rules, only p and g rules (see screenshot).
My auth model is as follows:
[request_definition]
r = sub, obj, act
[policy_definition]
p = sub, obj, act
[role_definition]
g = _, _
g2 = _, _
[policy_effect]
e = some(where (p.eft == allow))
[matchers]
m = g(r.sub, p.sub) && g2(r.obj, p.obj) && r.act == p.act
Hi there, I am facing issues with the Casdoor integration of Casbin.
I tried Casbin and came up with a simple RBAC with resources model that I wanted to try in Casdoor, and it doesn't work, because the g2 rules aren't taken into account, is it intended ?
Does the Casdoor integration of Casbin lacks features compared to the standalone version (e.g. RBAC works only with g but not with g2) ?
Thanks for your help.
