
fab7817
Fab
To be quite more precise, once I made an Enforcer (including the correct model/adapter), I don't see how to use them using Casdoor's permission system 🙂
Thank you, I've read the docs. Following it, does "Enforcers" and "Adapters" in the Casbin docs refers to "Enforcer" and "Adapter" in Casdoor?
I'm quite confused between theses two. If I'm right, Casdoor implements Casbin so I should follow Casbin docs in order to handle my permissions?
Hello! Me again, I'm trying to get how the permission/adapter system works. Any exemple how to restrict some API routes to given users? As "user1" got a "RO" role with a permission attached that restricts him to only use GET methods..
I will look into it tommorow, but so far haven't found anything weird. When using network inspection, frontend's api calls are identical wether setting the org on top right or not
I will try to request the API directly and see what'sup
I'm the first one to encounter such issue? 🙂
I mean that if I use the same name as the one provided built-in (on application boot), it does work
But if I change it towards "user-model-test" it won't
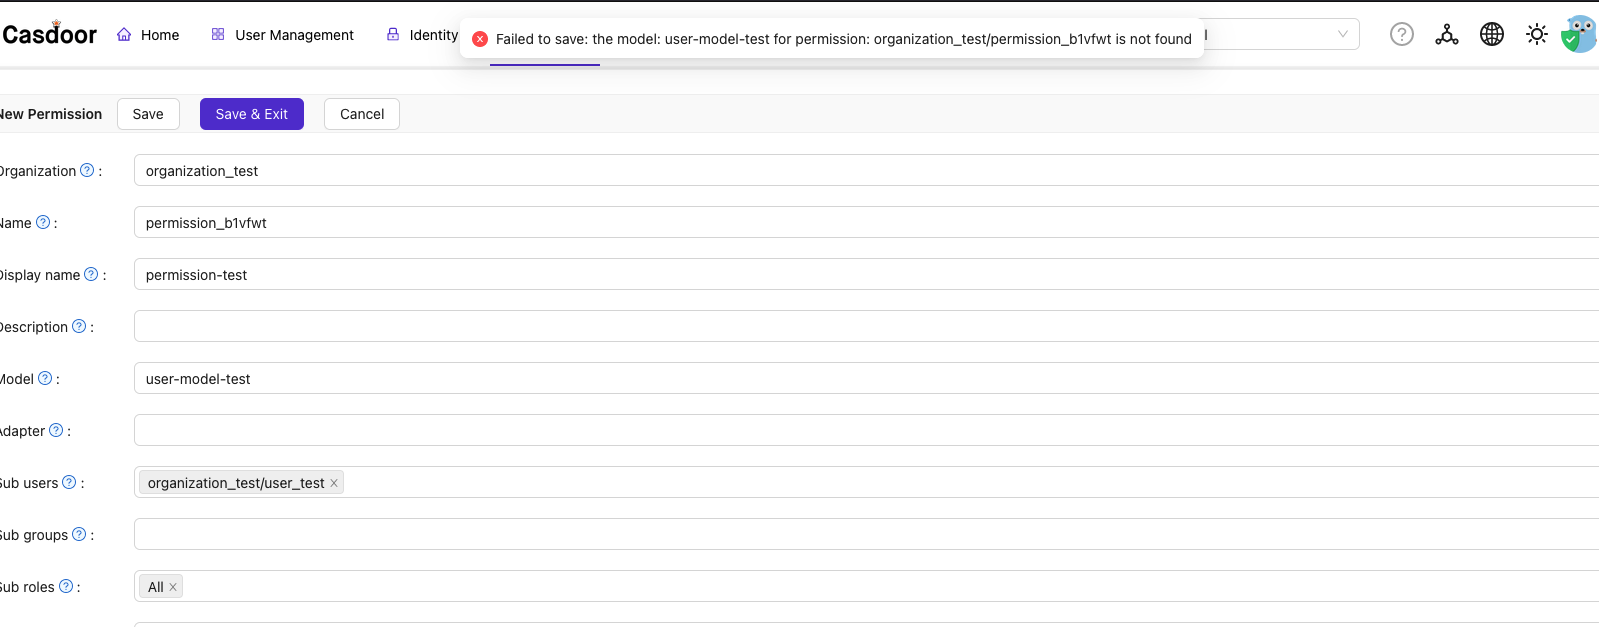
Edit: if the org is selected top-right of the UI, it does work. Problem happens when "all" is selected. I'm able to reproduce it multiple times so it may be a bug in the UI

I actually succeed using "user-model-built-in" as a name for a new model :
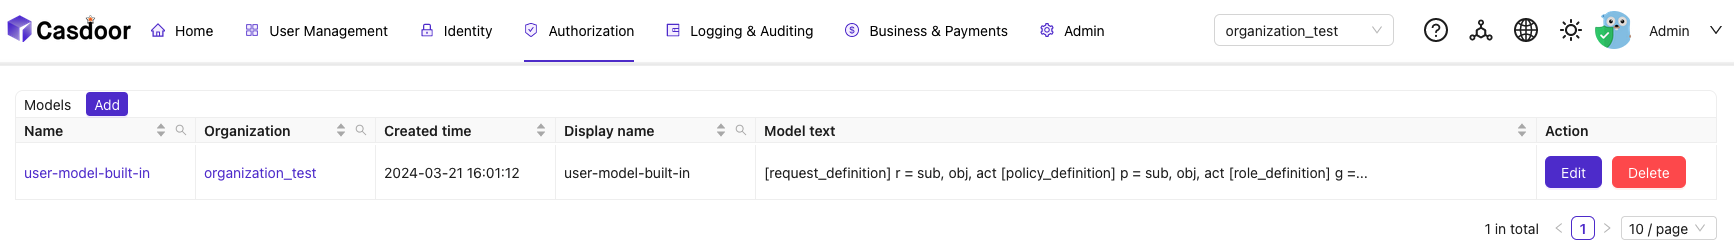
Is it a normal behavior ?
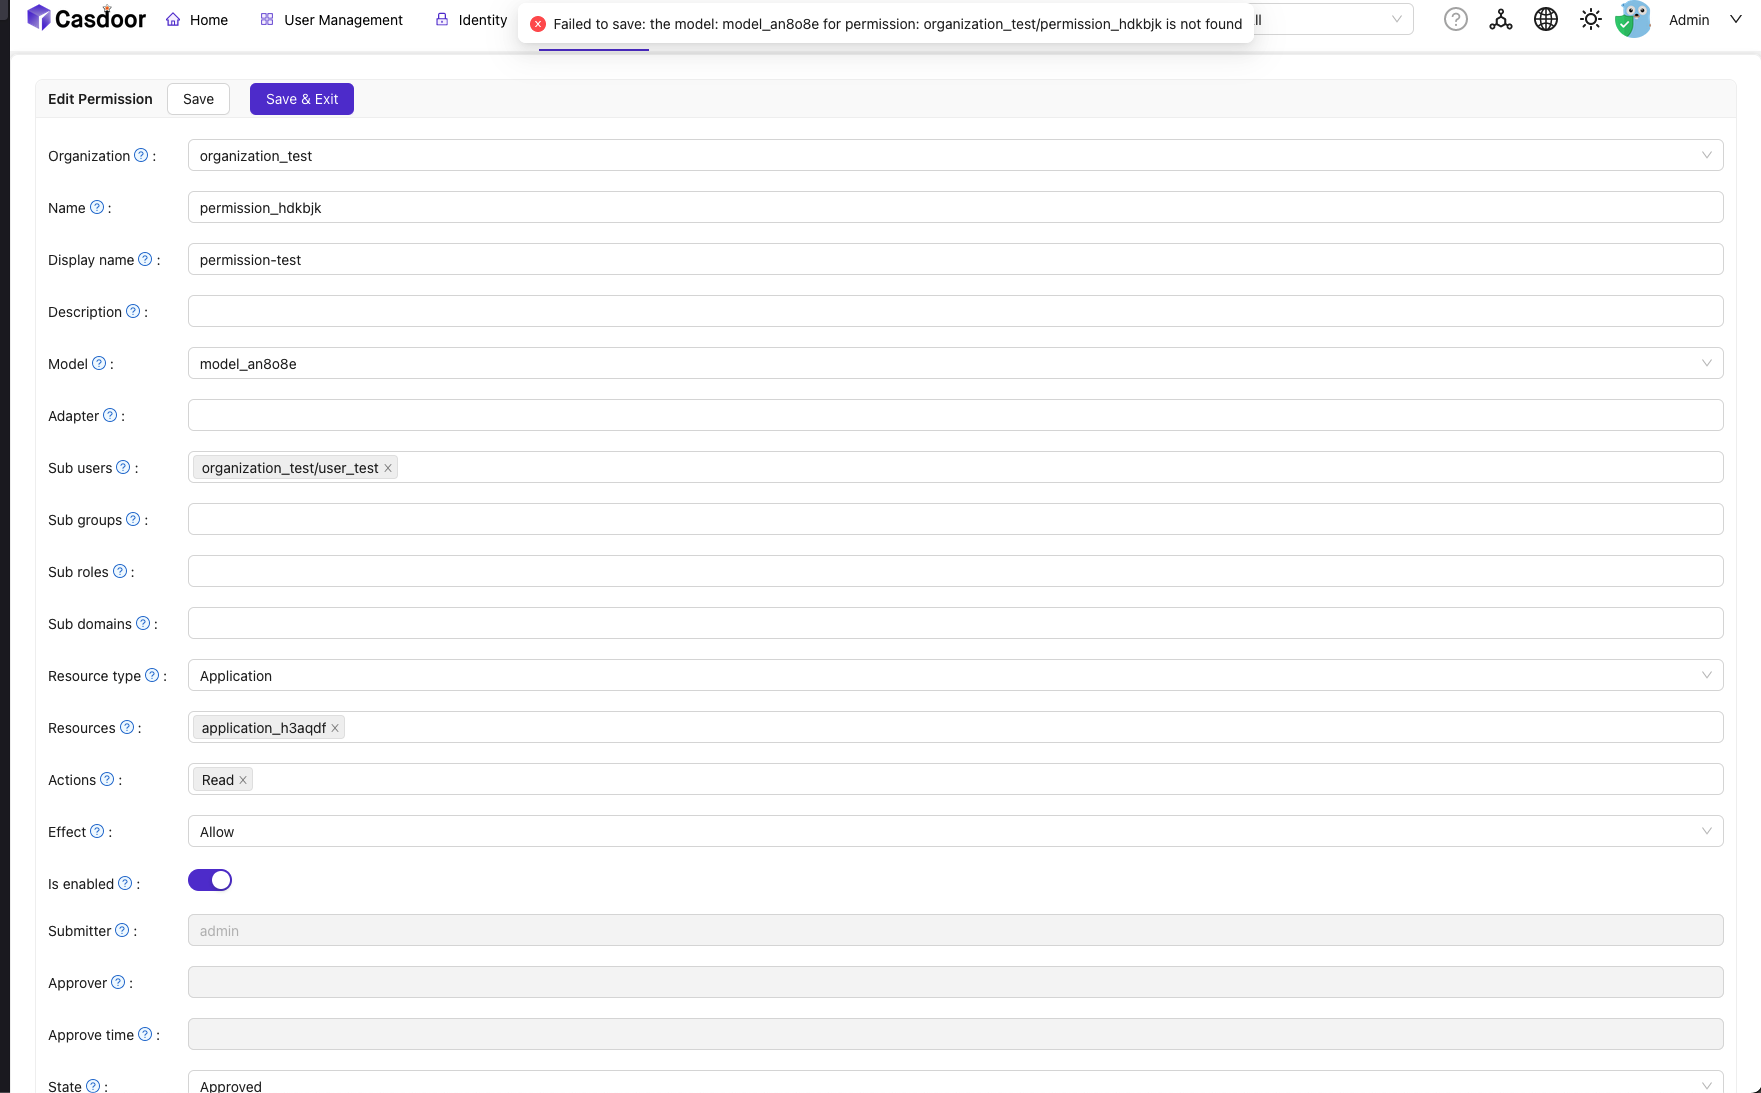
(model is just a copy paste from the user built-in one)
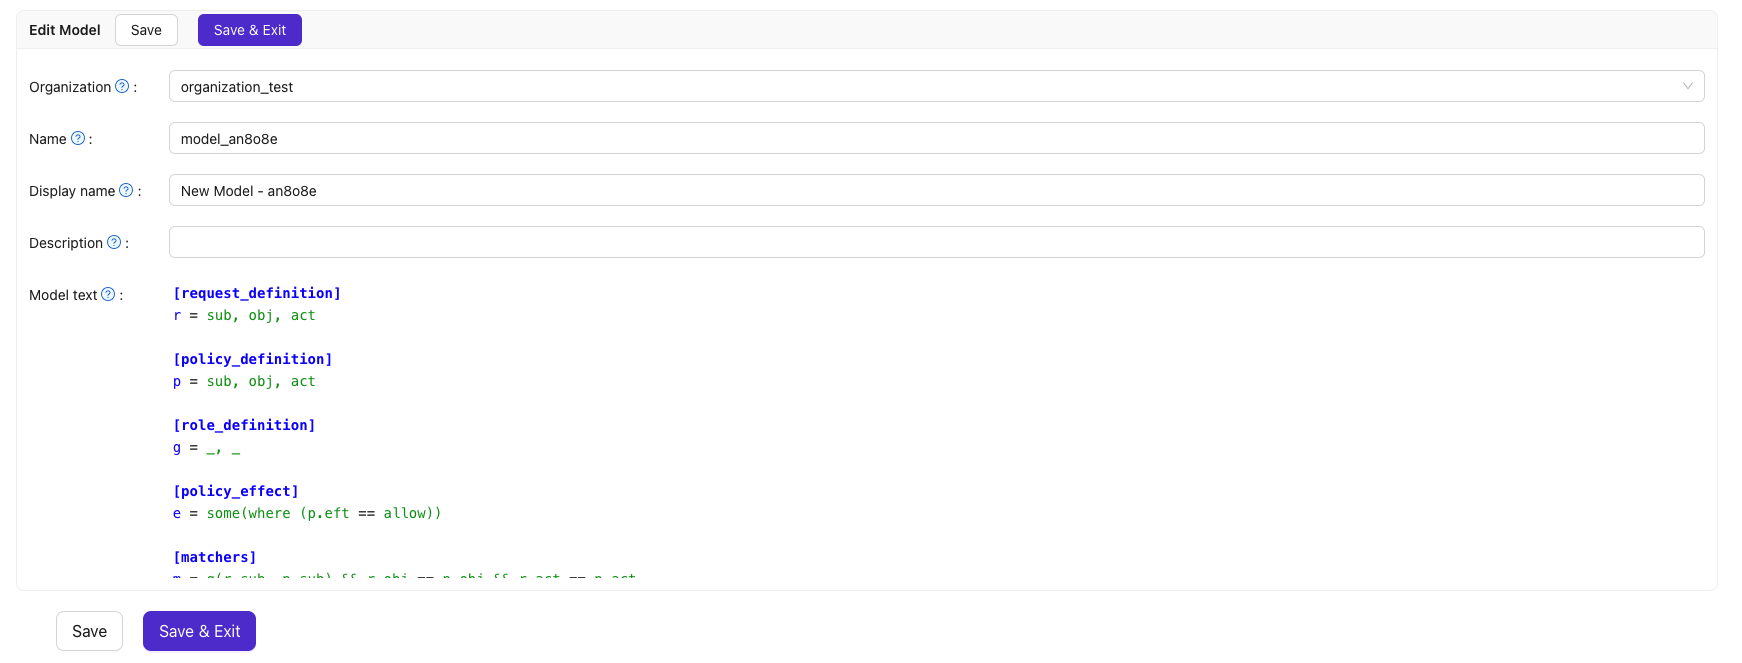
I can add models using built-in organization withouth issues
Hello! I'm reading on casbin's doc that we are unable to edit models at run time -> https://casbin.org/docs/model-storage/ . But on the casdoor's UI, I see some options that make me able to create/update new models. I'm asking this question because I'm struggling creating new permissions using models created from UI (getting "model canno't be found" error). I'm I missing something here? thanks 🙂
