
Looks like sql adapters in python keep columns null and those in rust keep them not null. @hsluoyz do you know of a python sql adapter that keeps it non null or rust sql adapter than keeps it null ?
Hey folks so I am using a combination of pycasbin to create policies and casbin-rs to read the policies -
My current table looks like the following -
My model file -
`
[request_definition]
r = tier, role, tag, act
r2 = role, act
[policy_definition]
p = priority, tier, policy, tag, act, eft
p2 = priority, policy, act, eft
[role_definition]
g = _, _ # role - policy mapping
[policy_effect]
e = priority(p.eft) || deny
[matchers]
m = (g(r.role, p.policy) && (r.tier == p.tier p.tier == "") && (r.tag == p.tag p.tag == '') && (r.act == p.act p.act == '')) r.role == 'superadmin'
m2 = (g(r2.role, p2.policy) && (r2.act == p2.act p2.act == '')) r2.role == 'superadmin'`
How ever when I load the policy for casbin rs, I get the error -
thread 'tokio-runtime-worker' panicked at 'called Result::unwrap() on an Err value: AdapterError(AdapterError(SqlxError(ColumnDecode { index: "6", source: UnexpectedNullError })))', fennel/src/auth/casbin.rs:47:14
any ideas ?
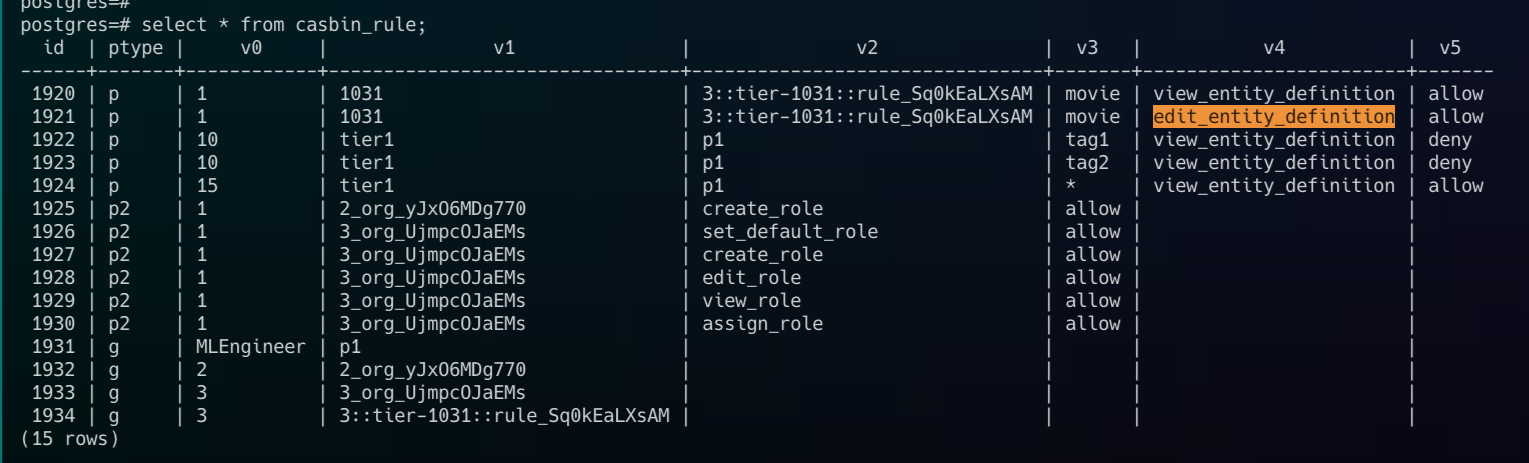
I have a feeling that for p2 kind of policies it is expecting some value for v5 ( the the 7th column ) but it is null ?
@weshuiz13 are you answering my question or is it a seperate question ?
Hey folks I am trying to create a RBAC model where users get mapped to a role, a role can consist of multiple rules and a rules contains multiple permissions and in the end I want to query for user -> resource , so as you can see there are multiple hops involved.
The model I wrote looks as follows -
// Kind refers to org / tier name
[request_definition]
r = kind, sub, tag, act
// rule is a specific rule identifier
[policy_definition]
p = kind, rule, tag, act
[role_definition]
g = _, _, _ # entity, entity-role mapping
g2 = _, _ # role-rule mapping
// check if there is any matcher that provides allow
[policy_effect]
e = some(where (p.eft == allow))
// find me roles that match this user, and then check if there is a rule that matches this // role which allows for this obj/tag and action
[matchers]
m = g(r.sub, role) && g2(role, p.rule) && r.tag == p.tag && r.act == p.act && r.kind == p.kind)
But the above matcher does not seem to work. How do I specify find a role that matches the users and see if the role has a rule in it for which the permission is provided.
The role variable essentially is a free variable which Casbin needs to figure out?
Is this not possible ?
