
Hey there! I am currently despairing at what to do. I am trying out Casdoor in an attempt to switch from Authentik + Zitadel. However, even at my first task to use Casdoor as an IdP for Forgejo (a Gitea fork) failed miserably, and I do not know what to do. I read the docs and googled around, but could not find a solution.
This is what I did:
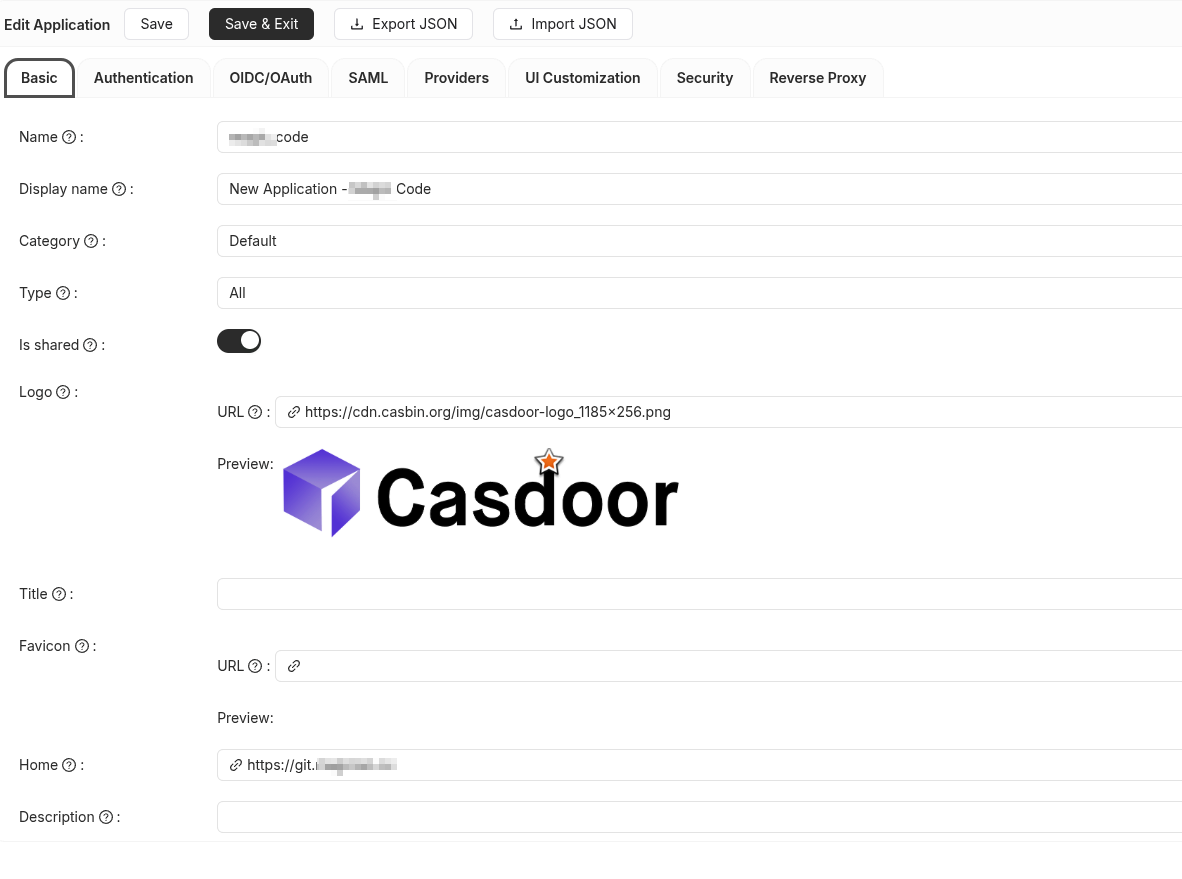
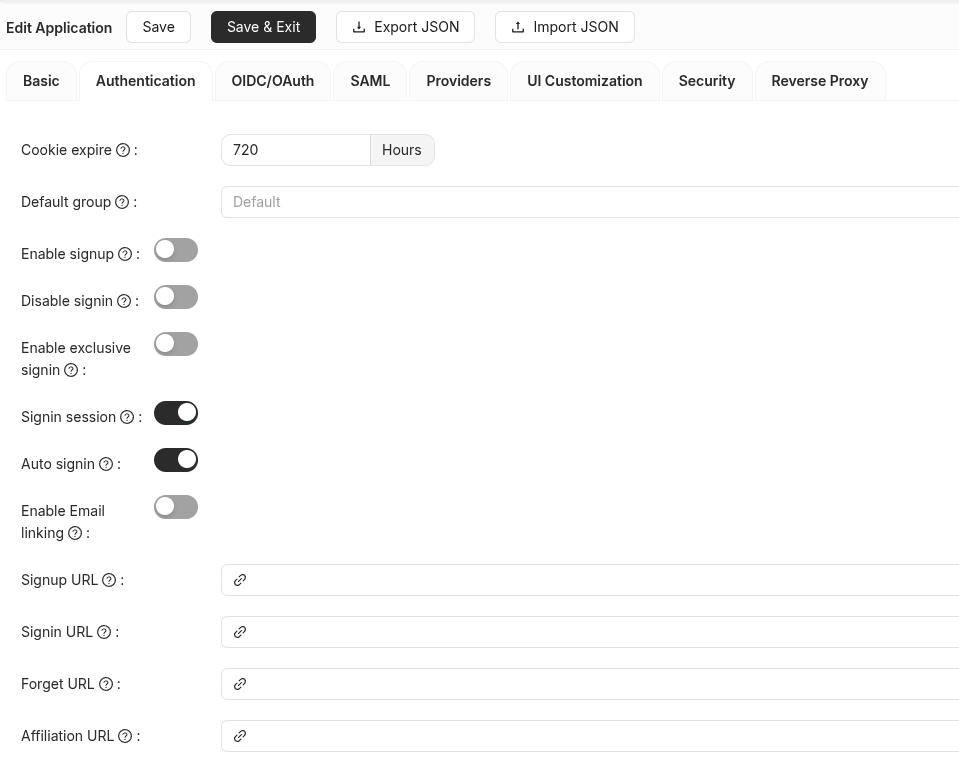
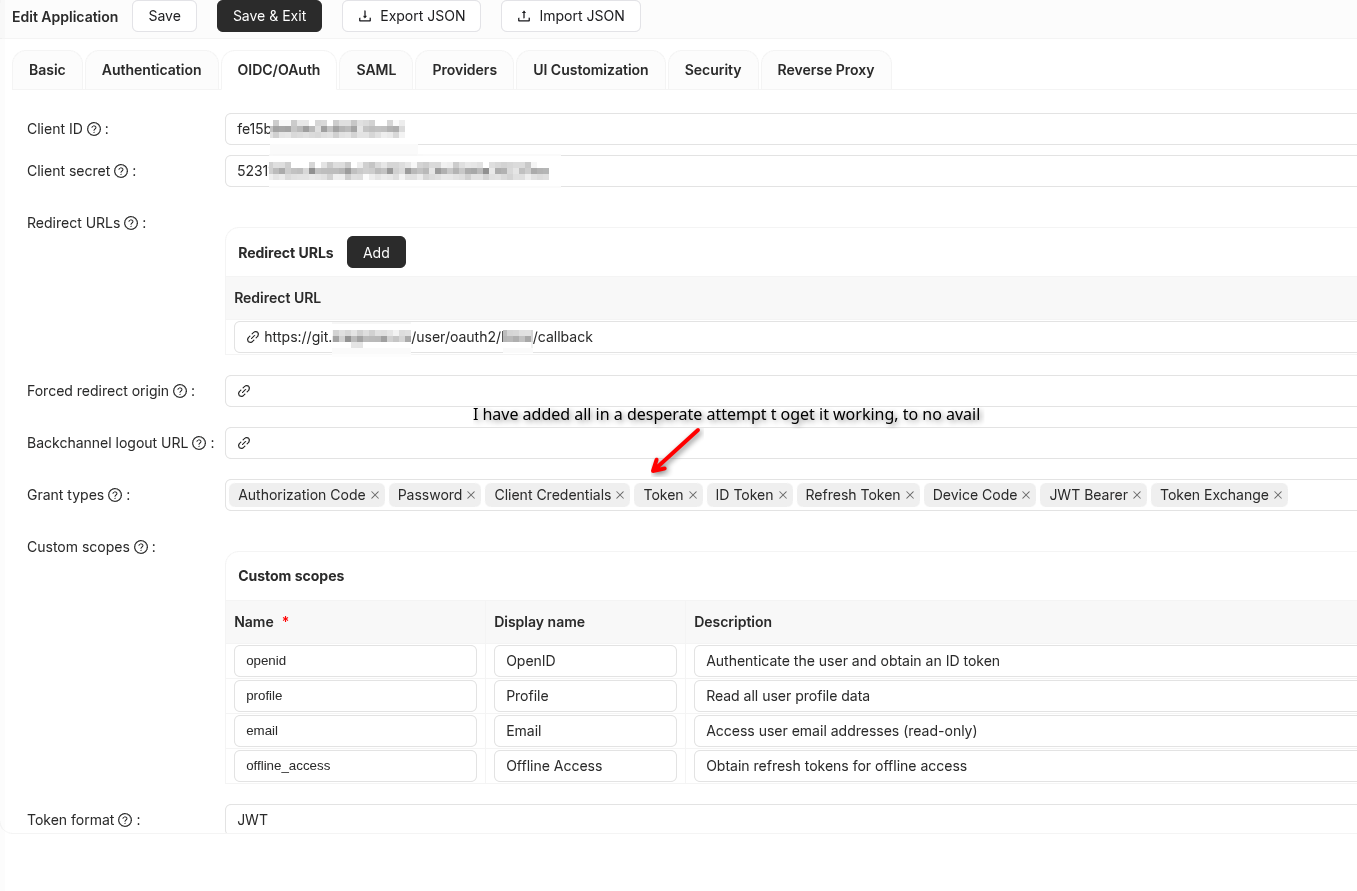
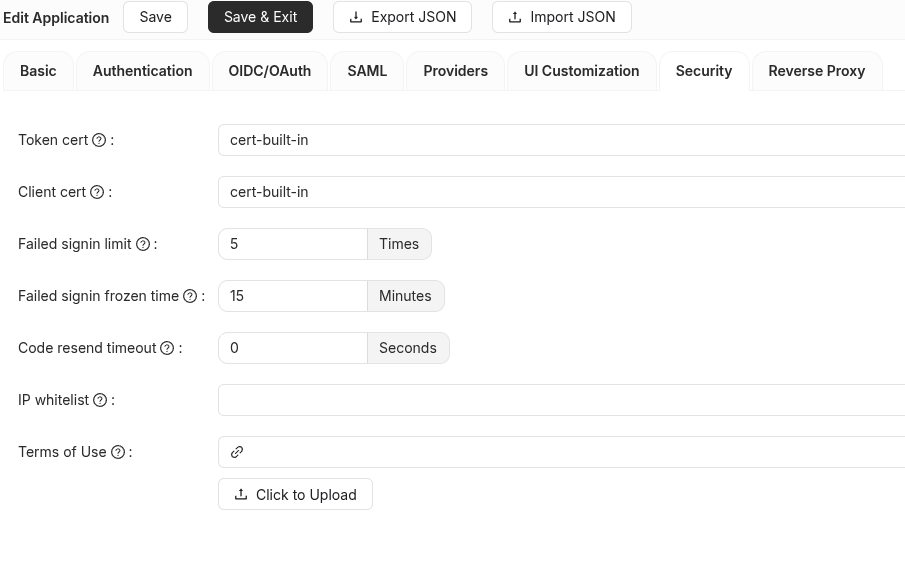
- Setup an application -> Under authentication set "Signin session" and "Auto signin" -> Set the Redirect URL to the <forgejo_instance>/user/oauth/<app_name>/callback -> added scopes "openid", "profile", and "email"
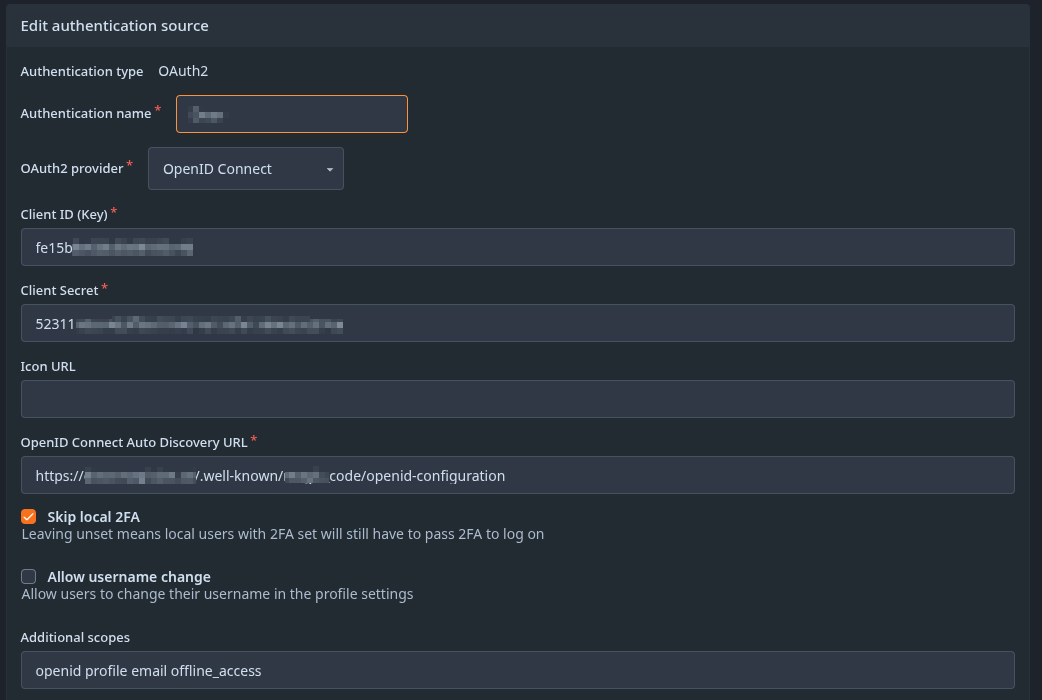
- In Forgejo: Added new authentication source -> Type 0Auth2, Provider "OpenID Connect" -> Key and Secret from the Casdoor application -> Auto-discovery URL to <casdoor_instance>/.well-known/<casdoor_app_name>/oauth-authorization-server (tried with openid-configuration as well, results in the same outcome) -> Added "openid profile email" to addition scopes
Yet when I try to authorize with it, all I get from Forgejo is an Error 500 with the message "UserSignIn, oauth2: error validating JWT token: *** in token does not match client key"
I already tried to play with the "Type", setting it to "OIDC" and "0Auth", with no change in the result. Same with the "Token Format" and "Token Signing methods".
I'm pretty sure it's not a problem from Forgejo's side, since that worked with basically every IdP I've tested so far
Any thoughts and help would be appretiated ^^

