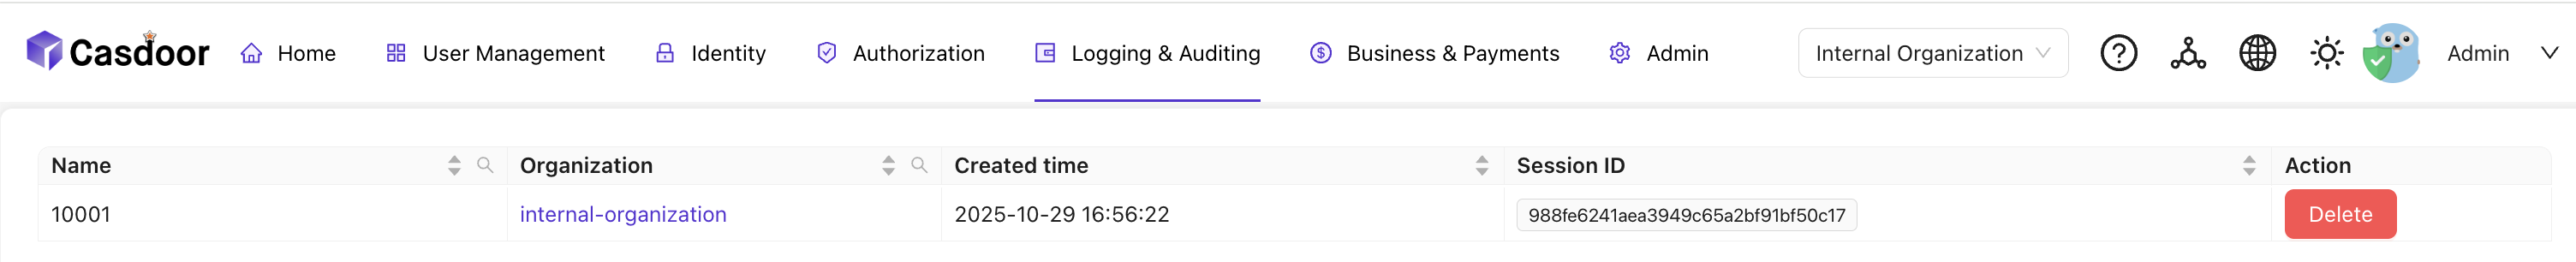
Hi, I’m testing the OIDC logout flow using the /api/logout endpoint by sending an id_token_hint. I noticed that while this call expires the access_token , the corresponding casdoor_session_id record under Sessions in Casdoor is not deleted.
Looking at the code, I found that session deletion uses Beego’s context (c.Ctx.Input.CruSession.SessionID()),:
owner, username := util.GetOwnerAndNameFromId(user)
_, err = object.DeleteSessionId(util.GetSessionId(owner, username, object.CasdoorApplication), c.Ctx.Input.CruSession.SessionID())
if err != nil {
    c.ResponseError(err.Error())
    return
}
Is this the expected behavior for /api/logout?
If so, what’s the recommended way to delete a specific casdoor_session_id entry in Casdoor when logging out through this endpoint?