
I believe this is also a bug or I'm doing something completely wrong, I copied the models, adapters and enforces from the casdoor default organization to my organization that I created to be able to access casvisor. but it doesn't access it, it simply only accesses it with the administrator user. On the demo site I tried to do the same thing but without success either.
model: "[request_definition]
r = subOwner, subName, method, urlPath, objOwner, objName
[policy_definition]
p = subOwner, subName, method, urlPath, objOwner, objName
[role_definition]
g = _, _
[policy_effect]
e = some(where (p.eft == allow))
[matchers]
m = (r.subOwner == p.subOwner || p.subOwner == "") &&
(r.subName == p.subName p.subName == "" r.subName != "anonymous" && p.subName == "!anonymous") &&
(r.method == p.method || p.method == "") &&
(r.urlPath == p.urlPath || p.urlPath == "") &&
(r.objOwner == p.objOwner || p.objOwner == "") &&
(r.objName == p.objName p.objName == "")
(r.subOwner == r.objOwner && r.subName == r.objName)"
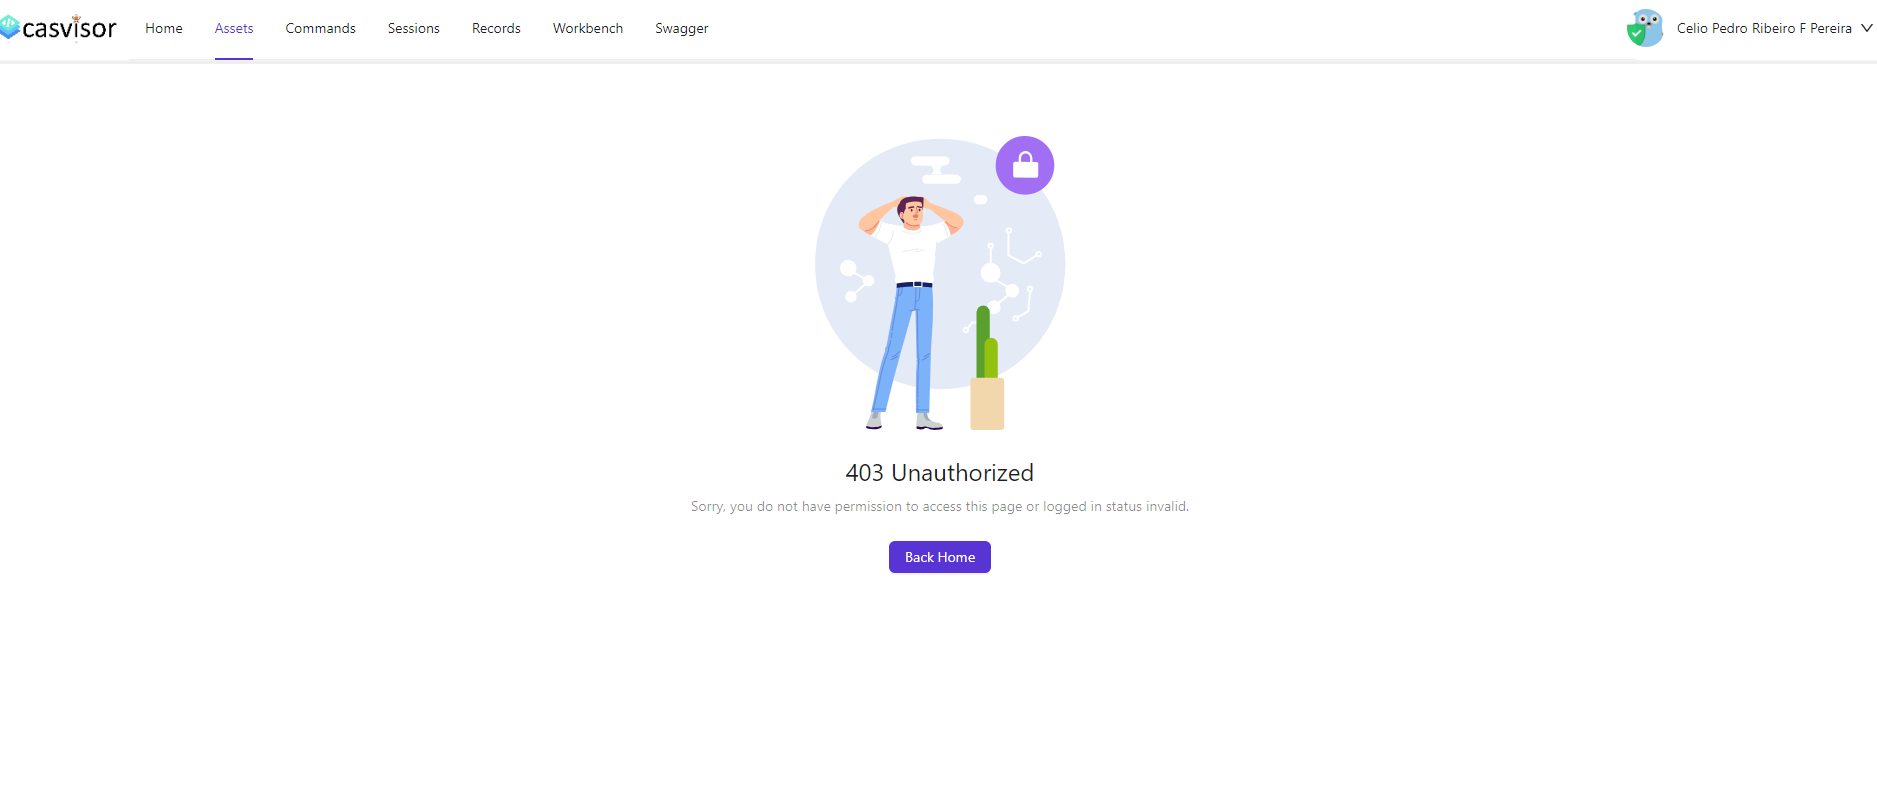
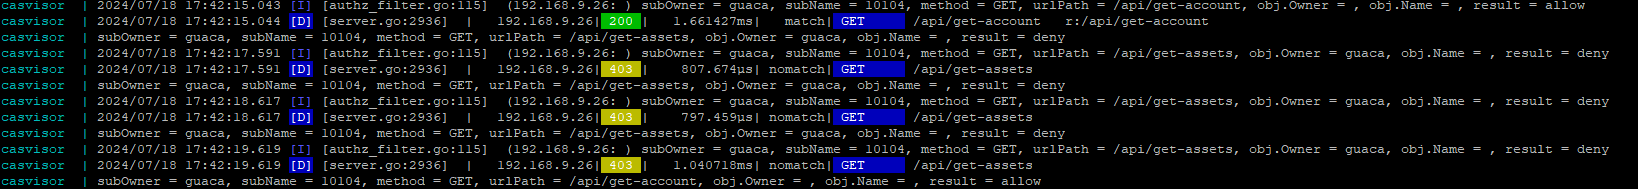
If you remove the "is admin" from the user hermann from the demo site and try to access casvisor, you will have the same error.

